If your site uses Field UI in drupal/core, this week's advisories include a remote code execution vulnerability in that module. It isn't directly exploitable with core alone, but I'd still check your installed version.
The fixes are in 10.6.19 / 11.3.19 / 11.4.10 / 12.0.0-beta2, depending on your branch. Those releases address all three core advisories:
drupal/core, Field UI: remote code execution, with the core-alone limitation noted above.
drupal/core, Link: insufficient sanitization of certain markup.
drupal/core, Navigation: insufficient attribute sanitization that can lead to cross-site scripting (XSS).
I read the new Composer advisories each week. For the week of 12 October 2026, these are the ones I'd check first on Drupal sites.
Hi y'all. I'm looking for advice as I transition from Webflow to WordPress (please challenge any of my thinking if you disagree with any of my below decisions). I have a background as a front-end designer/developer. My PHP knowledge is…nonexistent (thank goodness for Claude Code), but otherwise I'm fairly savvy and know just enough to be dangerous.
My plan is to use Bricks as the builder and I've figured out my monthly hosting. I think the biggest concern I have is managing updates/security — Webflow was all-in-one and WordPress is 100% not. We're going to have about 10 sites hosted simultaneously to start with, and probably 15 in the next 6 months, all with the same basic bones (all are for local small businesses with one woo commerce site):
ACF
Bricks for visual builder and forms
Complianz for GDPR
Here are my three questions:
What other plugins/workflows do I need to consider?
At the scale I'm working in (10 sites), is it worth doing something like WPUmbrella or ManageWP (or your best recommendation)? It seems like a lot of this is covered in my unlimited hosting plan, but I think that that requires me to still do many things one-site-at-a-time, whereas these tools enable me to 1-click across a whole fleet of sites that have the same basic functionality?
Is Google Site Kit worth it for easy client visibility, or should I simply manage that stuff through Google dashboards?
FYI, I have managed WordPress sites for my day job, so I'm familiar with the process and needs. But this is for my husband's company, and I only really have capacity to meaningfully update sites once a month with spot-checking/testing since it's effectively a side hustle.
Hey all. WP WAF Manager is my plugin for managing Cloudflare from inside WordPress. Until now it covered WAF rules, DNS, zone analytics, zone controls, IP access rules, security events and email routing.
Version 1.0.24.1 is out and it's the biggest update so far. It's grown from 8 modules to 14, and I rebuilt the website to show it all and the github link is: https://github.com/jaimealnassim/wpwafmanager
What's new
- Clients & Reports: link clients to their sites and email them a monthly report under your own agency name, logo and colors. It covers visitors, page views, threats stopped, cache speed, top pages and what Cloudflare blocked, in plain language. The plugin is never mentioned. You can send automatically on a chosen day and hour, or send by hand after a preview and a test.
- Zone analytics detail view: click any site for traffic charts, top pages, countries, status codes, devices and security events by action, path, IP and country, compared with the previous period. Table view and CSV export.
- Bot Control: set AI crawler policy (search, assistants, training), managed robots.txt and Bot Fight Mode across many zones at once.
- SSL & Insights: scan every zone for expiring certificates, Flexible SSL and old TLS versions, with one-click fixes for the safe settings, plus Cloudflare Security Insights.
- Alerts & Health: Cloudflare alerts for DDoS, SSL and origin health, sent by email, Slack or Teams, plus Health Checks on Pro zones.
- Turnstile: create widgets, rotate secrets and copy keys for every client site. Secrets are never stored.
- Page Rules migration: Cloudflare is retiring Page Rules. The plugin finds them on every zone and moves redirects and cache rules to their replacements in one click. Nothing is deleted.
- Zones and tags: tag sites as WooCommerce, Staging, Client and more, and pick them by tag when you deploy.
- Zone Controls upgrades: purge by hostname, prefix or cache tag, Smart Tiered Cache, security headers, and Under Attack Mode on every site in one click.
Still the same: everything is in the free version (GPLv2 on GitHub), it works on Cloudflare Free for nearly everything, and nothing loads on the front end. Pro is a one-time purchase that adds automatic updates and priority support.
A few notes:
- Security Events, Health Checks and Super Bot Fight Mode need a Cloudflare Pro zone. Blocking a whole country needs Enterprise.
- Deploying the WAF rules replaces the custom rules already on that zone, so check the Zone Rules tab first if you have your own.
Researchers at the National University of Singapore have developed a machine-washable electronic fabric that can turn clothing into an interactive graphical user interface. The prototype reportedly survived 50 gentle machine washes and 1,000 bending cycles, though it still relies on external batteries and controllers. The Register reports: The development could lead - at some point - to a "future in which clothing functions as a pervasive, multimodal human-computer interface," according to the study published in peer-reviewed science journal Nature this week. The paper shows someone interacting with computing devices using the sleeve of a wool sweater (no jokes about the Windows ugly sweater please, this is serious). The researchers, led by Singapore National University research engineer Fu Heng, claim this is a big leap forward.
"This fiber-centric approach shifts wearable electronics from flexible panels toward truly textile-native architectures, laying the groundwork for fabrics that visualize, sense, communicate and compute as naturally as the garments they inhabit," the paper says. The researchers claim to have developed a scalable process to make millimeter-thick fibers. Using lasers to strip the insulation from specific spots on the thin copper wires, they attached light-emitting chips to the exposed sections, creating electrical connections to the chips. Thousands of chips were connected to the wires with extreme precision using this process.
The fibers were then fed into a transparent plastic tube, and made pressure-sensitive by adding two strips of a compressible, conductive polymer into a second longitudinal channel in the tube. The paper says they could make fibers 10 meters long using this method, and that they are thin and flexible enough to be woven into or attached to fabrics. The researchers were also able to add "peripherals" such as a microphone, a speaker, a temperature sensor and a light sensor.
Frustrated by intrusive ads, sluggish interfaces, and data tracking, smart TV owners are using AI coding tools and open-source projects to strip unwanted software from their televisions and build customized home screens. The Verge reports: Several vibe-coded TV-debloating projects exploded in popularity over the weekend. Cleanyourtv (known as tv-vibehack until the 19th), tv-detox, and dumbtv all claim to accomplish similar things -- remove sponsored ads, debloat the TV so it runs faster, and block unwanted data collection that tracks what you're watching -- without hacking, or rooting, the TV. By default, they all also replace the TV's built-in app launcher with simpler ones. Many users are going a step further and vibe-coding their own replacement launchers, like the Pokemon one below.
Most of the projects we've seen so far focus on TVs that run on Android and Google TV operating systems (such as TCL, Hisense, Sony, and older Amazon Fire products), using existing developer modes and the Android Debug Bridge (ADB) to tweak settings and apply (and remove) packages. According to the GitHub pages, they can also work with some Fire TV products that use a custom fork of Android (although likely not on the new Vega-based Fire TV Sticks). Because they use built-in developer tools, they don't require root access or firmware hacking, and they're reversible. Even projects that totally change the look of the interface just use Android's ability to install custom launchers -- in many cases with an assist from Claude Code or a similar tool to create the new launcher, too.
Greece has passed a law banning children under 15 from social media platforms beginning January 1, 2027. The legislation requires platforms to implement reliable age verification and parents to use government-backed apps to restrict access, with penalties for noncompliance under the EU's Digital Services Act. Engadget reports: "It would have been very easy to do absolutely nothing today and wait for the perfect European law. But the challenge is here. Children are sinking into the internet every day, and I believe a responsible government must do what it is obliged to do," said Greece's digital governance and AI minister, Dimitris Papastergiou.
The legislation was opposed by Greece's minority parties, so Mitsotakis used his majority government to pass the bill. The nation previously barred mobile phones in schools in 2024, and opinion polls show that the new social media ban for children is widely supported by Greece's adult population. Mitsotakis previously said that his government's "goal is to push the European Union in this direction as well."
SpaceX is reportedly seeking access to at least 80,000 cellular tower sites across the U.S. as it prepares to launch Starlink Mobile as a fourth nationwide wireless carrier. "We will be building out our terrestrial networks so there's broad-based connectivity anywhere that SpaceX and Starlink are allowed to operate," Musk said during SpaceX's earnings call this week. Satellite launches plus spectrum acquisition "will pave the way for Starlink Mobile to become a major mobile carrier in the US," he said. Bloomberg reports: One of the companies they're in talks with is Crown Castle, which, along with American Tower and Vertical Bridge Holdings, are among the largest owners of cellular towers. When asked on a Wednesday earnings conference call whether Crown Castle is discussing leases with SpaceX, Amazon.com or other satellite-based telecom providers, Chief Executive Officer Chris Hillabrant said, "You can assume that we're talking to all parties." He declined to discuss specific customer details.
Mobile networks rely on antennas placed on towers across the country to transmit wireless signals. Carriers such as AT&T Inc., Verizon Communications Inc. and T-Mobile US Inc. typically lease room for their equipment at the tower sites because it's more cost effective than owning and maintaining them, in part because the facilities can be shared. The value of the deals with SpaceX could reach into the billions.
When I started my postion as a Drupal Web Developer I inherited a very poorly maintained Drupal site. It was on Drupal 9 when I started, a week before it went EOL. It took me a year to clean it up enough to make the jump to D10, and that was with a lot of help from my predecessor, who we had to bring in on a consulting fee, and while he was great and wicked smart, he was not a great teacher. I've been in my position for 3 years and have been so bogged down in front end content management that I haven't had time to do anything other than regular D10 patches. Now we're looking to jump to D11, since D10 is going EOL, and this new PHP nonesense is driving me up the wall trying to figure out how to fix all this without torching the site.
At this point I'm looking for a company who can come in and clean up all the wonky database mess we have, figure out what packages are being used, and basically clean up the back end of the site so I can have a clean build to work with. Who can I reach out to for a consultation and figure out how I can get this site back to a manageable build?
I've been building WordPress sites from Figma designs using Claude Code, and while the initial implementation has gotten much faster, getting everything production-ready still takes a surprising amount of time.
For those using AI in real client projects, what part of the process still takes the most time or manual effort? Maybe you have a repo to share?
UpdraftPlus paid, premium version used to back up my sites within 3-5 minutes at the most to Google Drive AND Updraft Vault. Now it just runs and runs indefinitely and never completes unless I stop it, turn off or disable the UpdraftPlus feature and just use it as I did with the free version and only backup to Google Drive. If I only backup to Google Drive, it's done in 33-4 minutes again without stopping or slowing down.
When will it work as normal again? I'm wondering how long it should take them to recover after the hack. It just has not worked the same since the hack and I'm trying to get an idea on when it might be able to run backups again without it taking hours to run or timing out.
The New York Knicks reportedly sent employees a fake offer of complimentary NBA championship rings as part of an internal phishing test, requiring anyone who clicked the link to attend mandatory cybersecurity training. "Congratulations, your Employee Championship Ring is here," the email said. According to The New York Times, Madison Square Garden employees who clicked that link "were forced to attend a mandatory cybersecurity class to help satisfy some of [owner James] Dolan's growing cybersecurity concerns." Ars Technica reports: The offer wasn't implausible, either. "Typically, most employees for NBA teams receive rings, even if they are not as fancy and expensive as the ones the players receive," wrote Joe Vardon, senior NBA writer for The Athletic, which was bought by The New York Times in 2022 and then merged into the parent news organization. Vardon's article was primarily about how Knicks assistant coaches did not get rings on Tuesday when the team raised its first league championship banner since 1973. The assistant coaches were handed boxes without rings inside, though they are expected to receive rings later on.
"Ring orders, designs, and measurements can take time, and not every coaching staff for every defending champion gets its rings on ring night... The Knicks assistants were told they would receive championship rings eventually, but many longtime employees at Madison Square Garden, including some who work in the Knicks' business operations, will not receive rings at all, team sources told The Athletic," Vardon wrote. MSG employee hopes were raised "at the end of September when the Knicks sent an email to a long list of employees, which gave recipients a first glimpse at their would-be championship rings," Vardon wrote. The email included "a graphic of two differently styled rings" that the lucky employees could supposedly choose from, the article said.
"(Employee name), this one is on the house. MSG is issuing a complimentary employee championship ring. The same jeweler, the same craftsmanship, personalized with your name. No cost to you," the email said. "There are two designs to choose from: Championship Gold and Garden Classic. Reserve the one you want below." Vardon wrote that "multiple team sources" confirmed the email was a phishing test. It's not clear how many employees clicked the link or whether any of the employees who received the email will eventually get some type of championship ring. We contacted the Madison Square Garden Sports organization with these questions and will update this article if we get a response.
Diplomatic organizations in Central Asia have been targeted by a sophisticated new Unified Extensible Firmware Interface (UEFI) bootkit called BlackX.
The activity, which singled out diplomatic entities in Tajikistan, Uzbekistan, and Turkmenistan in early 2026, is suspected to be orchestrated by a China-linked state-sponsored hacking group known as APT41, Kaspersky said in a technical report
An anonymous reader quotes a report from TechCrunch: AI agents left to explore a virtual island without a specific task began inventing challenges of their own. MIT researchers say the behavior bears the hallmarks of play. The researchers put 13 AI agents called Eko, each running on Claude Opus 4.7, alone on a simulated desert island for 30 hours. They describe the experiment in a paper posted on arXiv, a site where researchers share studies before peer review. Afterward, they gave the agents specific challenges, like getting as many objects as possible onto the island's tallest rock spire. The Eko agents that had spent those 30 hours playing generally beat identical agents that had never set foot on the island.
Today, developers decide in advance what AI should practice and what counts as success. The researchers see this technique -- exploring without a goal -- as a different way for AI agents to learn skills, especially skills that could one day be used to control robots. "We normally develop artificial agents by deciding in advance what they should practice, what they should optimize, and what counts as progress," the researchers write in their report. "Play suggests another regime: give an agent a sufficiently rich and safe world, let it choose what is interesting, and allow useful knowledge to accumulate from the history that follows." UC Berkeley cognitive scientist Eunice Yiu told MIT Technology Review she was impressed with the findings but that more evidence is needed to determine whether AI models are genuinely playing. "It could be the case that the models are genuinely playing, but we don't know based on the paper," says Yiu. "If you only have the behavioral piece, it could be the case that they're just trying to abide by the prompt, trying to imitate humans."
MIT professor and coauthor of the paper, Phillip Isola, added: "It's not like this is a system that just suddenly magically decided to play. It's an artifact that learned from our culture, was trained by engineers at Anthropic, and was then placed on an island by us. It does things that surprise us and that are causally related to its future skillful behavior."
Ruby has released versions 4.0.9, 3.4.12, and 3.3.13 to fix three bugs in Onigmo, the regular expression engine built into the language. The bugs lie behind four critical security flaws that GitLab patched over the past month.
GitLab found that a specially crafted pattern could corrupt memory while Ruby compiles it, potentially leading to code execution on its own servers.
Ruby says any
Cybersecurity researchers have discovered an artificial intelligence (AI)-driven intrusion ecosystem run by affiliates of the INC and The Gentlemen ransomware groups.
Central to the operation is an "Autonomous Red Team Kill Chain Framework" referred to as Phantom. The threat actor is assessed to be Russian-speaking and functions both as an intrusion and data-extortion operator, as well as an
I recently released Veridis Fraud Guard for WooCommerce, a free, open-source plugin built around a fairly specific problem: repeat customers who place problematic orders, particularly Cash on Delivery orders that end up uncollected.
Instead of relying on automated fraud scoring or third-party services, it lets store owners maintain their own blocklist using email addresses, phone numbers, IP addresses, or email domains.
Depending on the selected mode, a matching checkout can be blocked, flagged with a private warning, or, for COD orders, placed on hold for review.
It supports both Classic Checkout and Checkout Blocks, HPOS, and runs locally on the WordPress server. No subscription or external account is required.
It's not an AI fraud detector, and it won't automatically identify first-time fraudsters. It's intended to give merchants more control over recurring problems they've already identified.
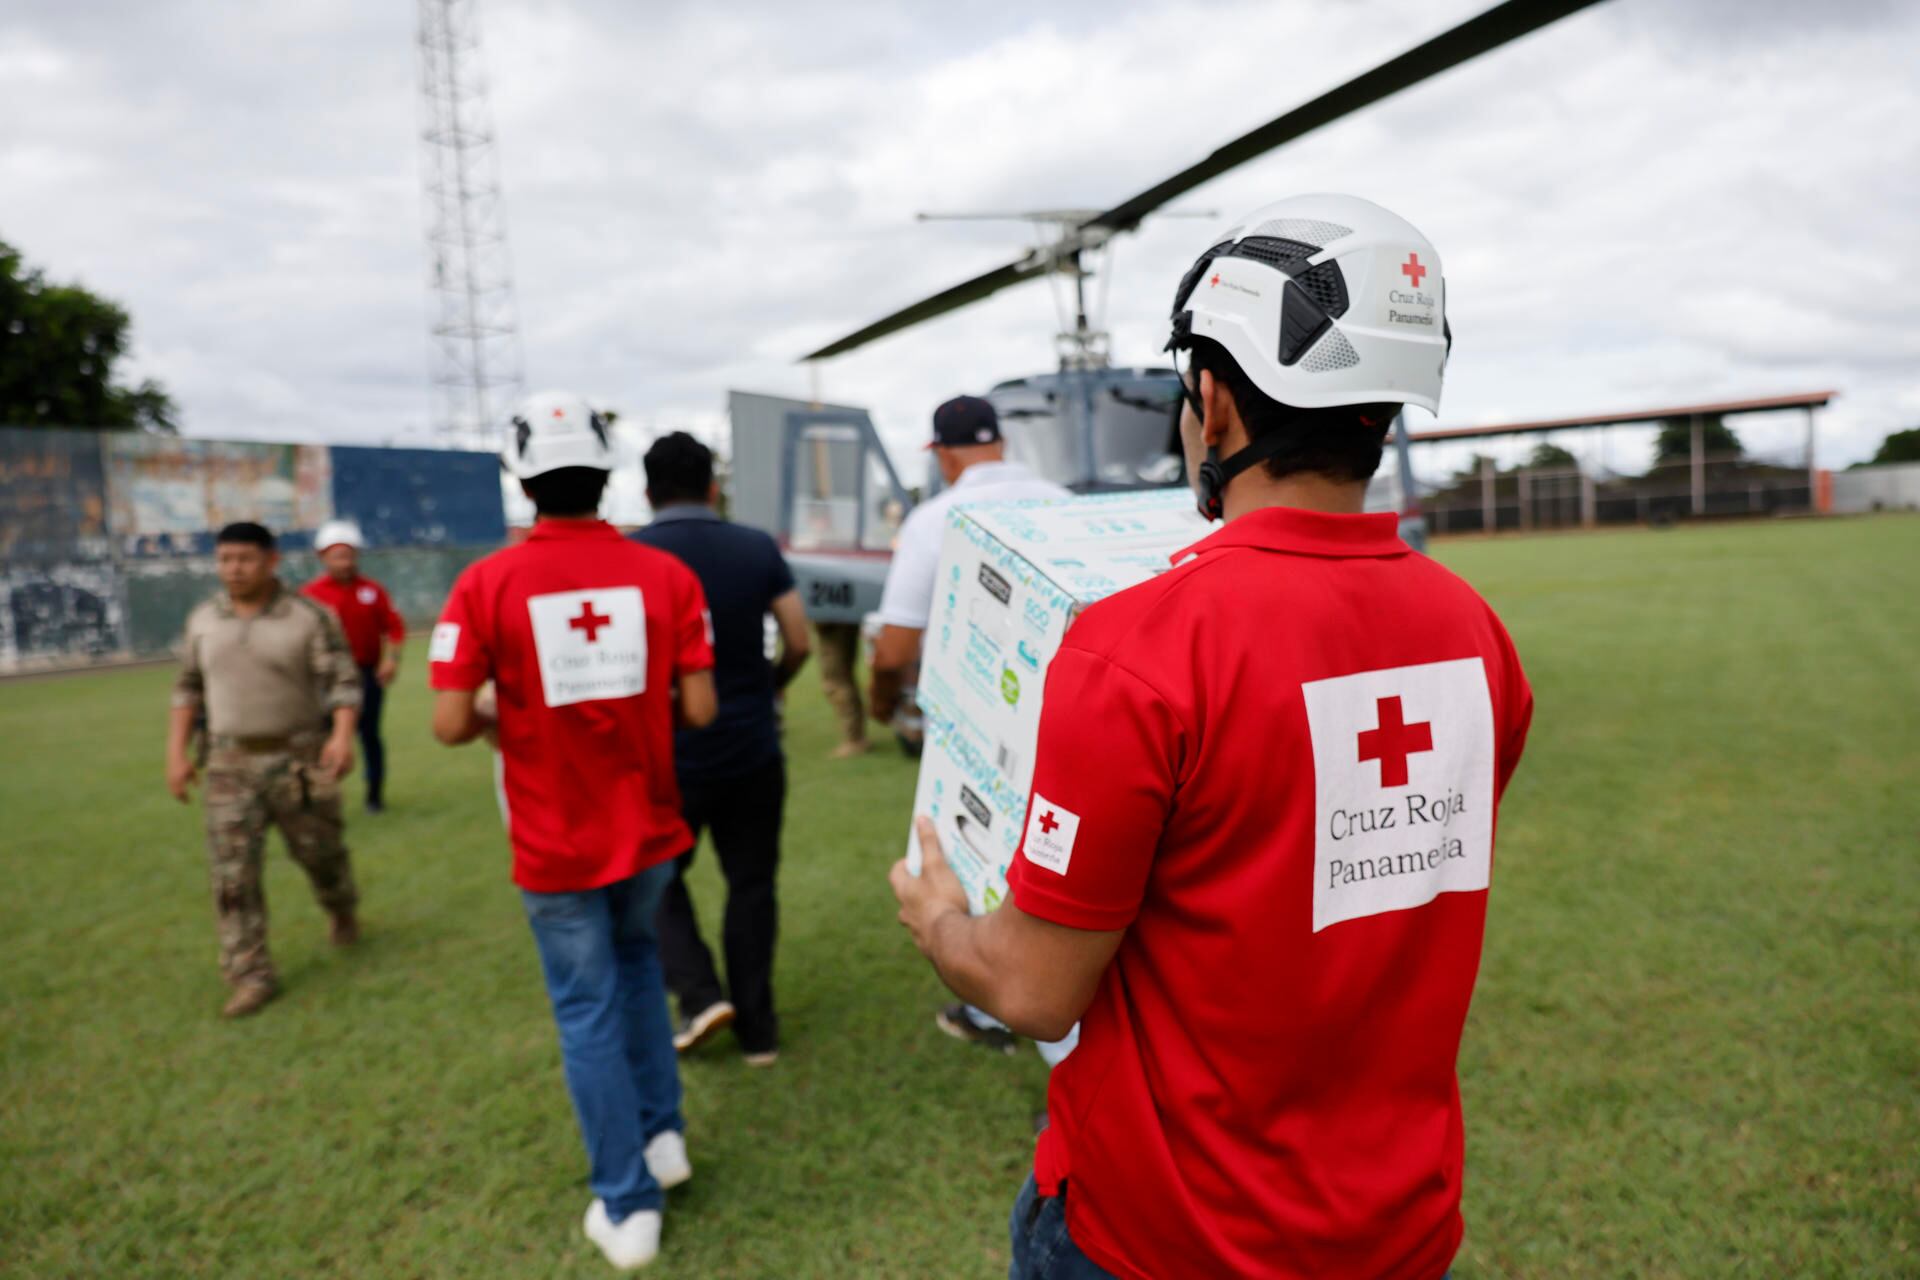
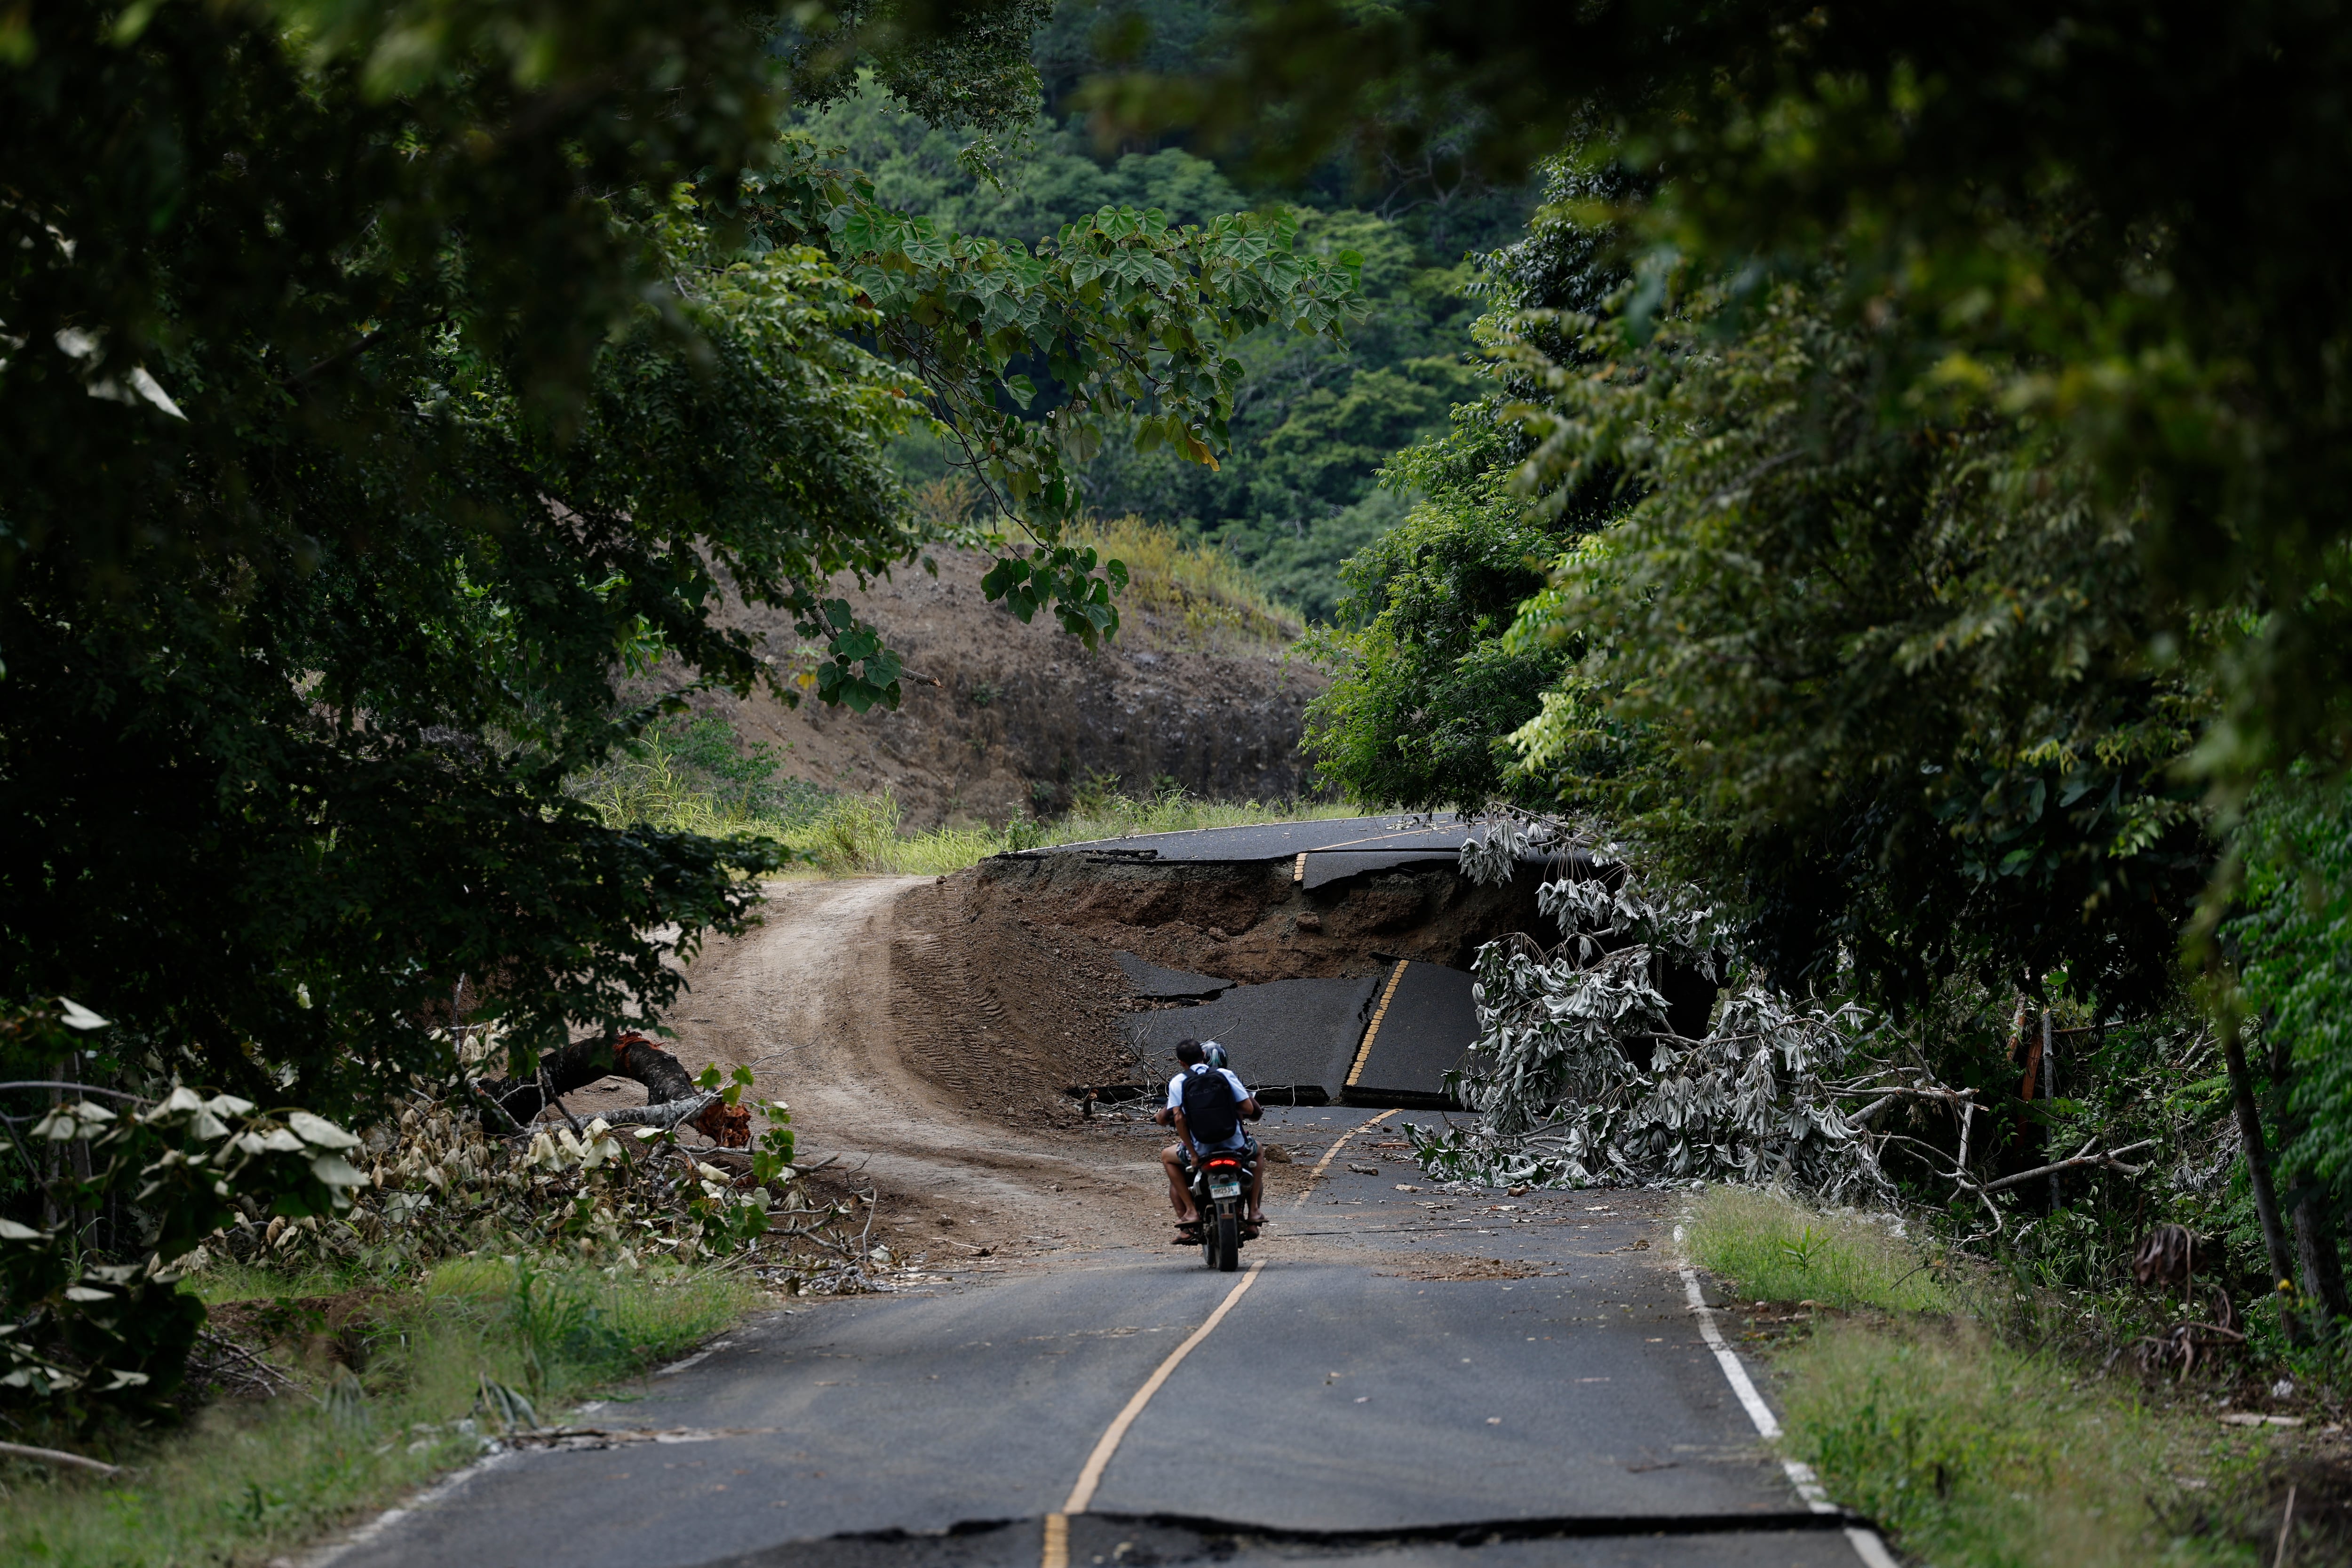
El terremoto del 9 de octubre en Panamá aceleró el uso de una tecnología que permite crear, gestionar, analizar, visualizar y compartir mapas y datos geolocalizados. El objetivo es hacer más eficiente el manejo de la información y coordinar mejor la respuesta en el terreno, evitando la duplicación de esfuerzos.
Así lo confirmó Raymundo Ortega, de la Cruz Roja Panameña, quien lidera desde este organismo humanitario parte del trabajo para poner en marcha una plataforma conjunta de datos abiertos. La información recopilada ya está siendo utilizada por los organismos de emergencia a través de los mecanismos de trabajo existentes, con el apoyo de profesionales de ESRI en el análisis de los datos.
Una vez completada, la plataforma centralizará la información de los distintos portales que reúnen datos, imágenes y otros recursos durante las emergencias. El objetivo es integrar información técnica y no técnica para facilitar la coordinación entre las instituciones y mejorar la respuesta ante futuros desastres.
“Cuando se presente otro evento categoría emergencia, [se podrá] saber cuál es la ruta”, comentó Marianne Amaya gerente de cuenta para ONGs y Educación de Esri Panamá que acompaña el proceso y habilitó para la Cruz Roja un sistema de respuesta ante emergencias. ESRI también proporcionó dos técnicos sénior para apoyar el análisis de la información.
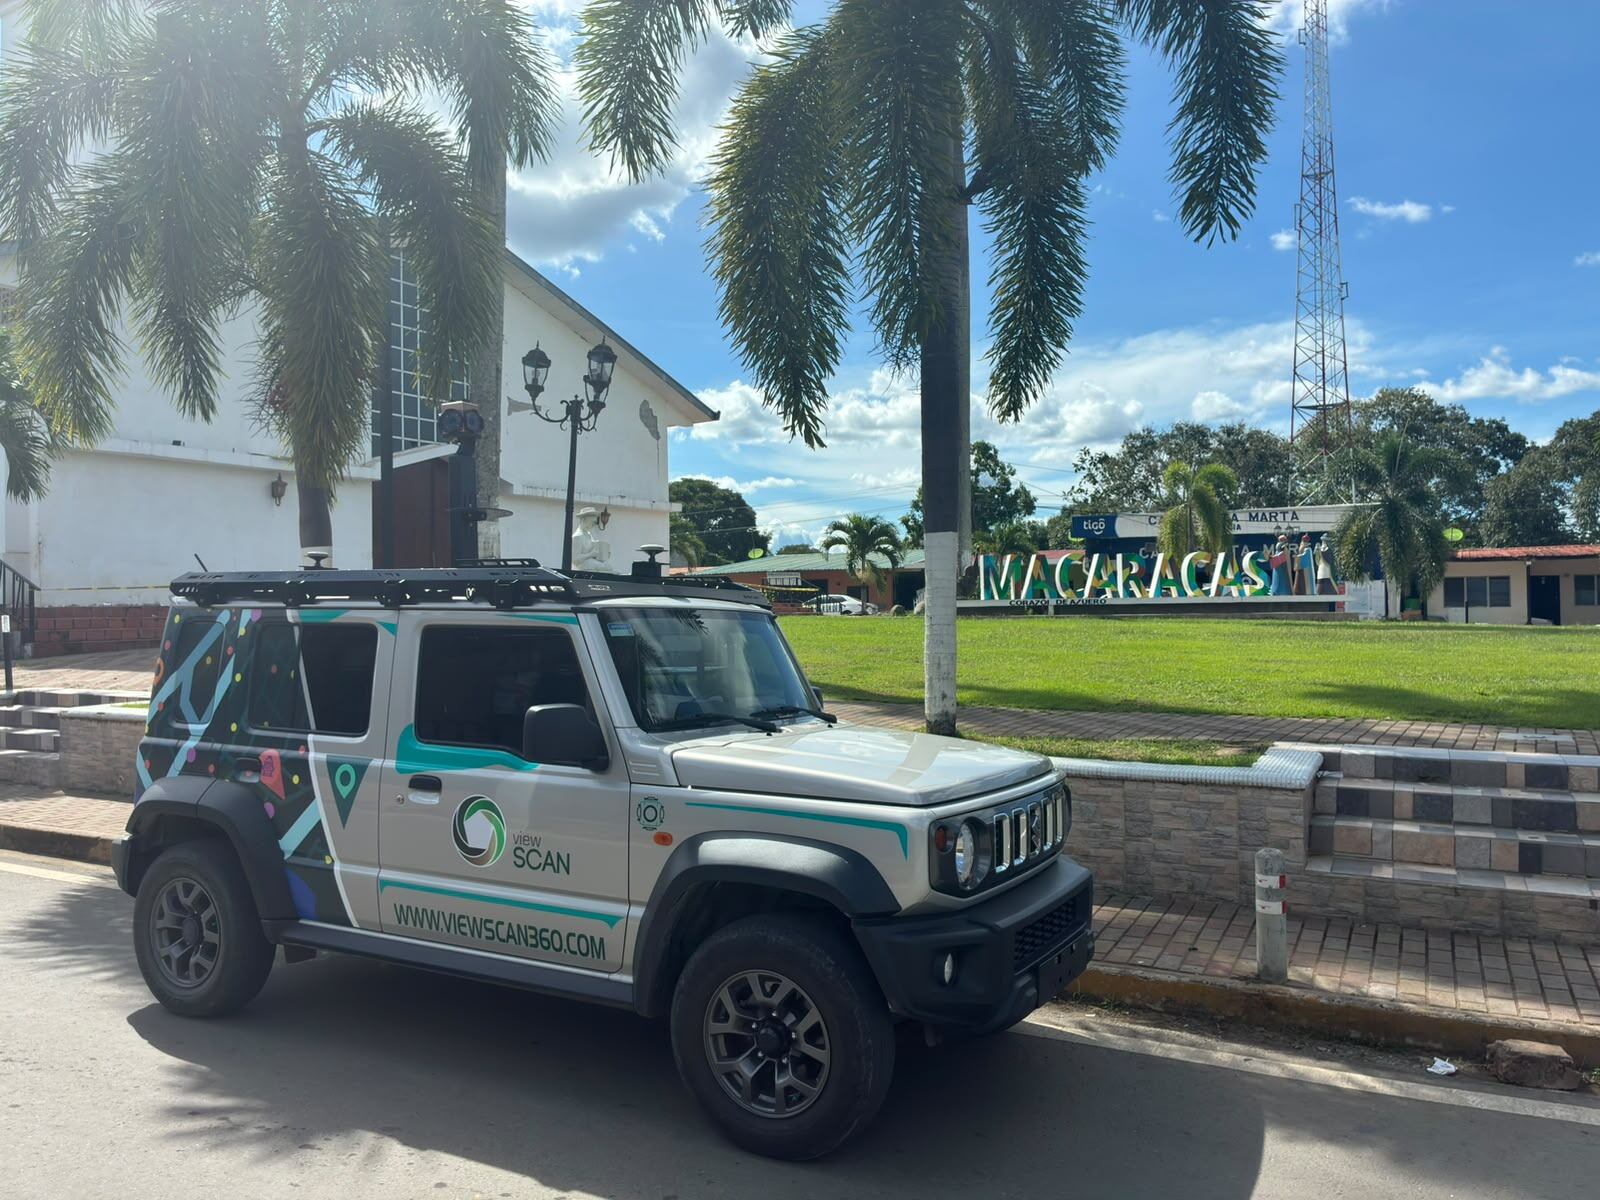
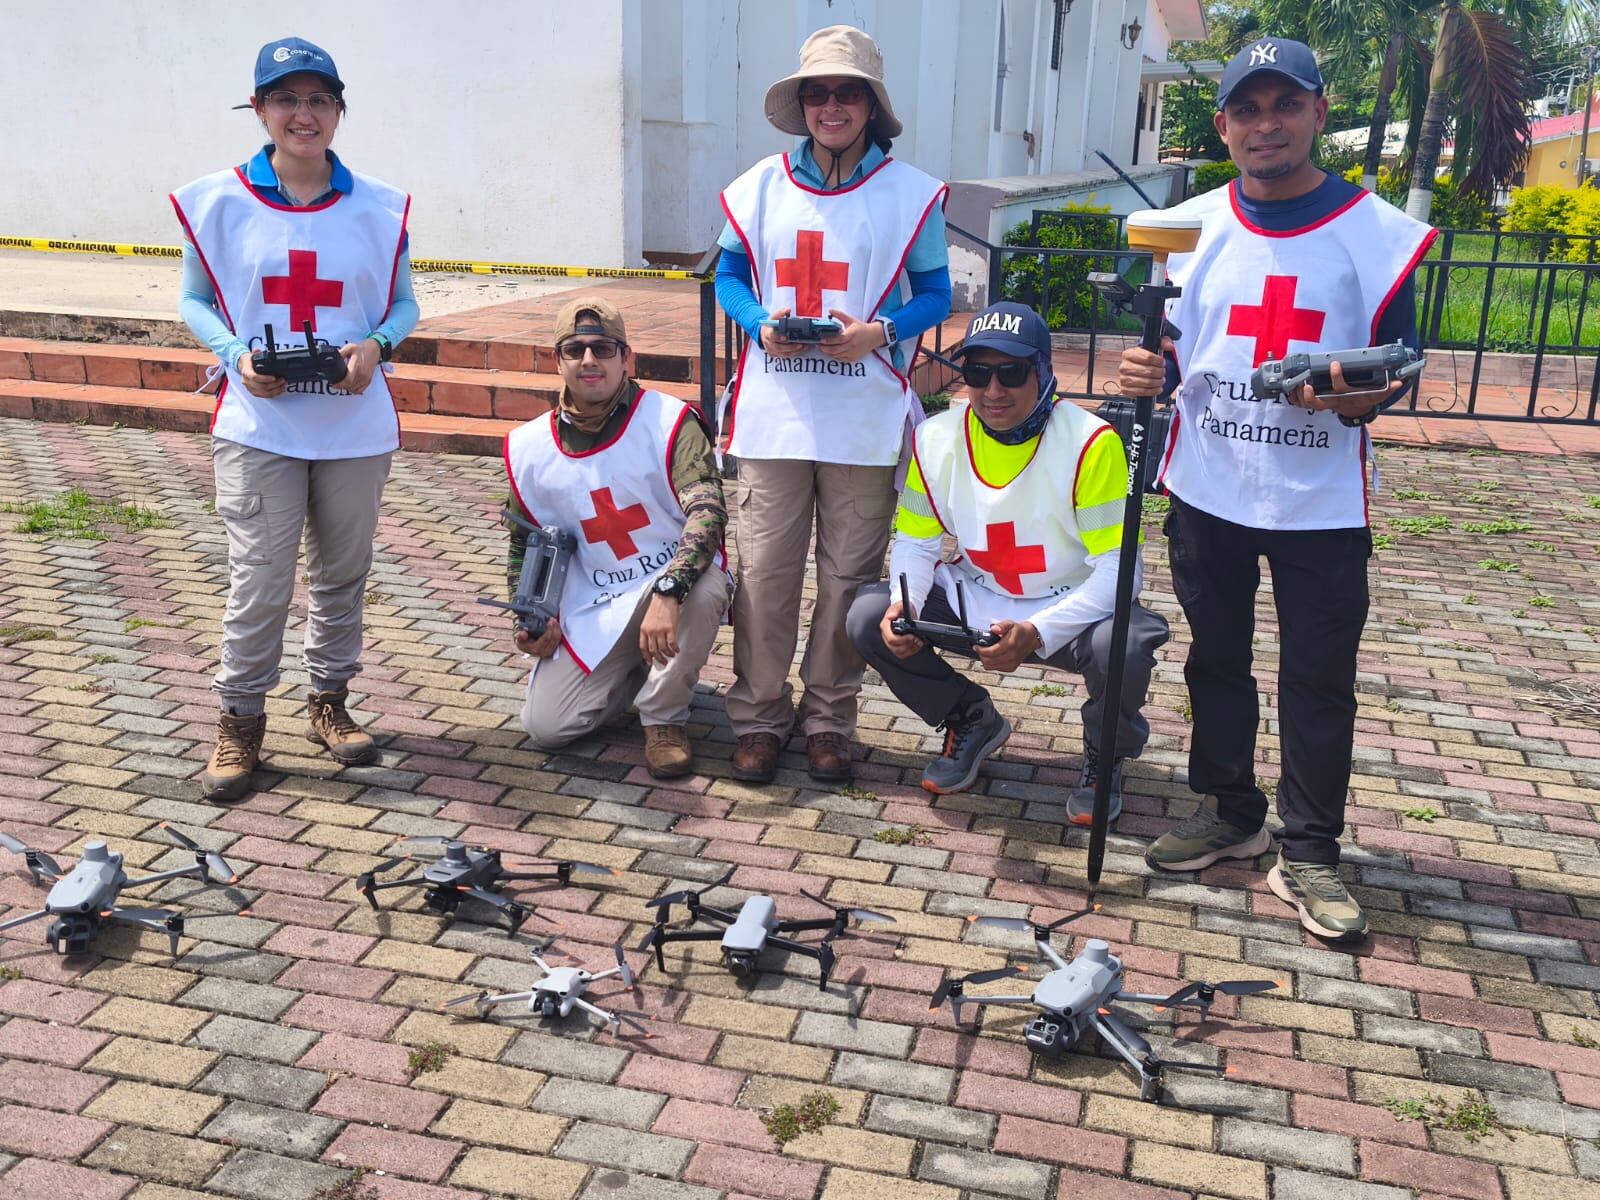
Ortega explicó que, mediante el uso de drones (Cobots Lab), el mapeo 360 (Grupo Tx) y recorridos realizados por voluntarios, se ha recopilado información sobre Tonosí y Macaracas. Ambas zonas, cercanas al epicentro, fueron identificadas como prioritarias para iniciar el trabajo por el impacto que tuvo sobre el terreno y sus infraestructuras el terremoto de 7.7 grados que sacudió la región de Azuero.
Este trabajo fue posible gracias a alianzas con las empresas mencionadas y al Movimiento de Pilotos de Drones Solidarios por Panamá, que surgió en respuesta a la necesidad de brindar apoyo y soporte a las comunidades afectadas por el terremoto incorporando la tecnología como herramienta para contribuir a la respuesta ante la emergencia, facilitar el acceso a información del territorio y apoyar las labores de evaluación y atención.
“A través de vuelos con drones se captó el estado de todas las vías, estructuras dañadas y se tiene la certeza de dónde hay escombros”, precisó Ortega, como ejemplo del trabajo que se está realizando. En Macaracas, en particular, se coordinó un trabajo que incluyó vuelos con drones y mapeo 360 en las calles, de manera simultánea.
Ortega explicó que, para evaluar los daños tras un desastre, el Sistema Nacional de Protección Civil (Sinaproc) utiliza una encuesta que también emplean el Cuerpo de Bomberos, el Ministerio de Salud y el Ministerio de Educación (Meduca).
“Con la emergencia que tenemos aquí en Panamá, el formulario que utiliza Sinaproc nosotros lo estamos usando también. Y de ahí entonces nace también hacer levantamiento un poco más allá, y consolidar toda la información en un solo punto y que sea de acceso para las instituciones o las entidades de respuesta”, afirmó.
El inicio
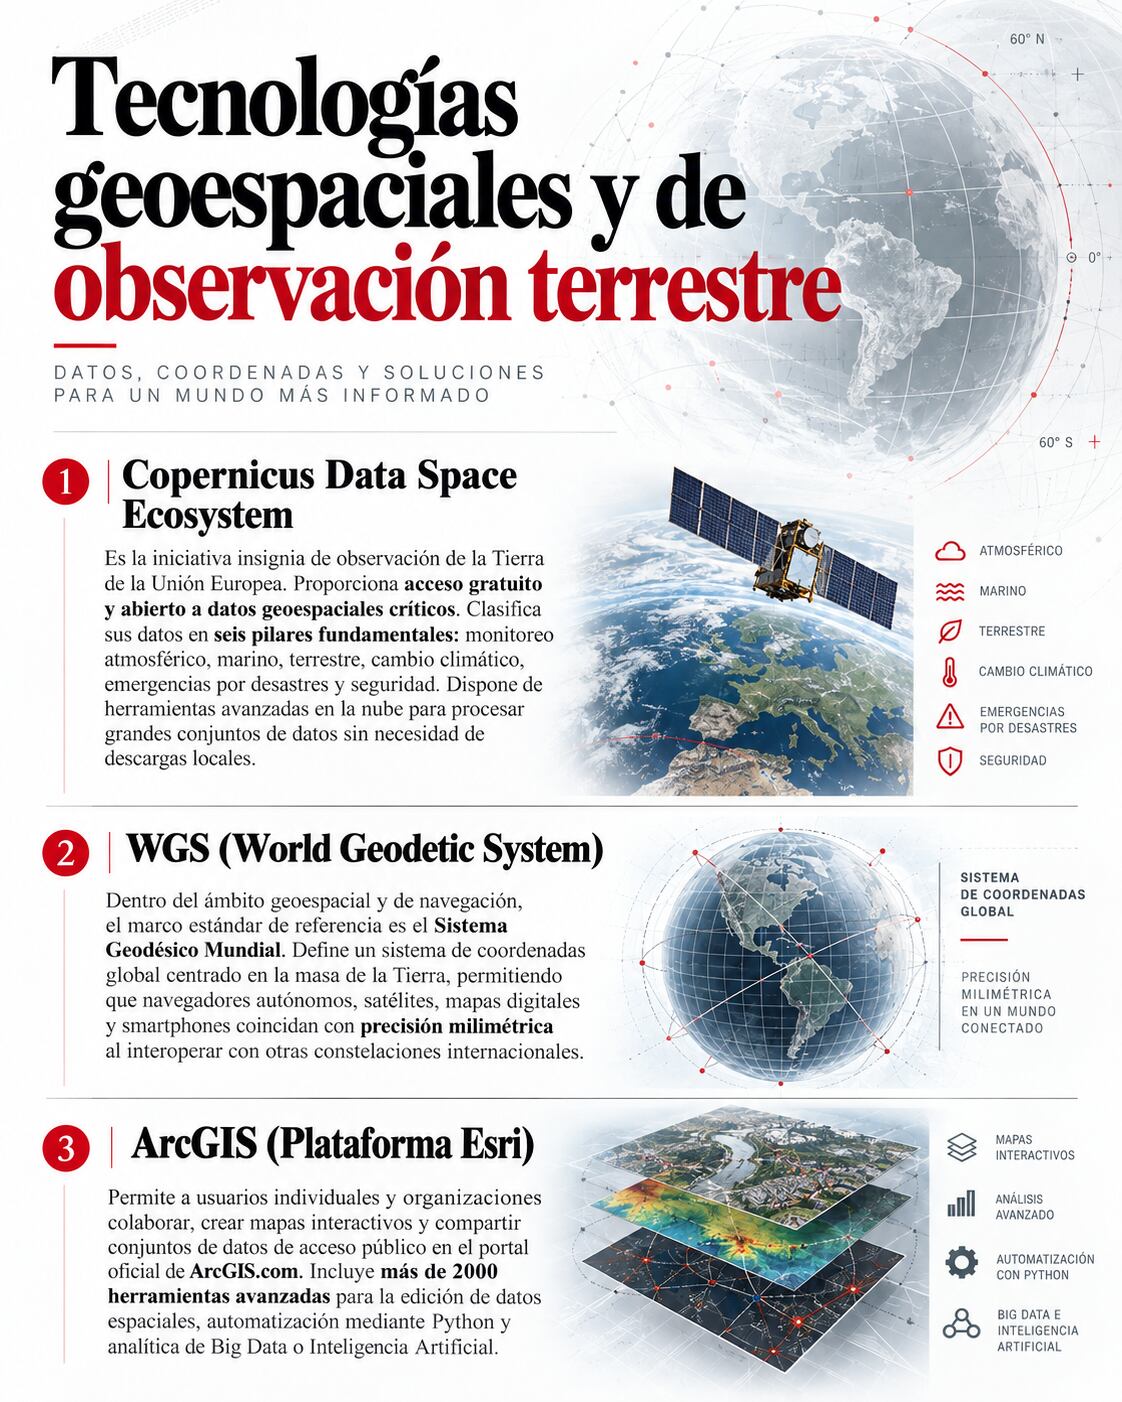
Hace unos cuatro meses, la Cruz Roja Panameña comenzó a familiarizarse con esta tecnología, de la mano de ESRI. La organización forma parte del Centro de Operaciones de Emergencia (COE), integrado por otras 45 instituciones y organismos de respuesta y seguridad. Estas herramientas, que llevan años utilizando empresas e instituciones gubernamentales, incluyen plataformas como Copernicus, WCGS y ArcGIS, entre otras.
Ortega destacó que, en emergencias anteriores, a menudo el personal de emergencia llegaba a una calle y descubría que otra organización ya había intervenido. Con la herramienta que han desarrollado, explicó, la información está unificada y todas las organizaciones pueden consultarla para coordinar la respuesta.
Así, a partir de junio sacaron las licencias necesarias y empezaron a capacitarse y, en octubre, cuando el terremoto azotó el área de Azuero decidieron utilizar la necesidad como generador de acción. Ortega relata que hicieron una convocatoria, seleccionaron voluntarios de acuerdo al perfil y se empezó el trabajo en los puntos de intervención, coordinando con los centros de operaciones de emergencia. Luego fueron a hacer el levantamiento de información geoespacial, que permite mejorar la evaluación de daños que se está haciendo a pie, ya que se genera un modelado de datos que está disponible para las instituciones cuando van a entregar la ayuda humanitaria. “Por ejemplo, si yo quiero reconstruir escuelas, ya tengo la encuesta que se hizo a pie, el sobrevuelo para saber el grado de afectación, datos estimados que me indiquen el costo aproximado de pérdida”, detalló. De esta manera, acotó, vamos viendo una respuesta más integrada.
El trabajo que aceleró el terremoto
En la mayoría de los puntos cercanos al epicentro del terremoto el equipo de trabajo ha logrado un 80% de levantamiento de la información con drones, lo que les permite confirmar lo que se realiza con personal a pie.
En tres días se recorrieron los puntos de mayor prioridad: isla de Cañas, Tonosí, Tonosí cabecera, Macaracas, Llano de Piedra, La Colorada. La Pitaloza —epicentro del terremoto— aún no ha sido mapeada con las tecnologías geoespaciales. Mientras tanto, ya comenzó la segunda parte del trabajo, que es el análisis para la toma de decisiones basada en evidencia.
La información está consolidada, centralizada. Eso permite dar una respuesta mucho más rápido, porque a veces cuando ocurren las emergencias [...] dejamos comunidades por fuera, porque no tenemos esa visión amplia de dónde hemos evaluado y en dónde hemos entregado.
Raymundo Ortega, Cruz Roja Panameña
El trabajo se hizo en coordinación con el resto de las instituciones y tras conocer que no existían mapeos de este tipo.
Como parte de la información ya recopilada está: cuántas familias y cuántas viviendas han sido afectadas, cuál es el nivel de afectación (total, moderada, leve o no tuvo), cuántas personas viven en la familia. Ahora, otro grupo de personas “que no estuvo en el terreno se encuentra procesando la información de imágenes, videos, moderación de datos o de estructuras, capas de antes con las capas de ahora”, indicó el técnico de la Cruz Roja Panameña.
El proyecto de la Cruz Roja Panameña va más allá de la actual emergencia. Estando en tiempos de paz, destaca Ortega, su objetivo es trabajar con las comunidades en la preparación para desastres, en el programa de brigadas escolares, incluso en programas de no violencia y de salud, hasta mapeo de zonas vulnerables en las comunidades que están cercanas a las sedes de este organismo humanitario, de forma que puedan integrar en un solo lugar todos los programas, todos los recursos y todas las acciones, a través de las coordinaciones internacionales.
De acuerdo con el informe más reciente del Sistema Nacional de Protección Civil (Sinaproc), del miércoles 21 de octubre, el balance preliminar registra 10,655 viviendas evaluadas, que involucran a 35,065 personas en análisis de necesidades. Además, 619 centros educativos y 120 instalaciones de salud con afectaciones.
Como parte de la respuesta a la emergencia, el organismo informa que se han habilitado 126 albergues que acogen a 5,628 personas; que se han movilizado unas 208,317 libras de ayuda humanitaria por vía aérea y al menos 365 toneladas por vía terrestre, con atención reportada en 175 comunidades.
Microsoft has revealed pay-as-you-go pricing for Xbox Cloud Gaming, with introductory packages costing $3.99 for 10 hours, $7.99 for 25 hours, or $11.99 for 50 hours. Starting in November, Game Pass subscribers will receive only 5 to 15 included cloud-gaming hours depending on their tier and will have to buy additional time -- even to stream games they've already purchased. Gizmodo reports: Back in September, before these changes were announced, you paid full purchase price for a game that isn't in the Game Pass library on the assumption that you'd be able to play it via cloud streaming. Maybe your hardware doesn't meet the specs for this fancy new game. Maybe your gaming PC exploded/got stuck on a ship/had a component fail. Maybe you just want to be able to play it in bed on your laptop. Whatever. Now you find that in addition to the cost of the game you bought, you're going to be paying by the hour to play it once your monthly allotment of hours is up. If this is you, I expect you're not particularly amused. Thankfully, Microsoft notes that the playtime you purchase "remains available until it's used," so you won't have to worry about losing any unused time between gaming sessions.
It is time to have a serious discussion about the creaking infrastructure that underlies Wordpress which allows:
Invisible Users
Invisible Admin Users
Invisible Posts
Invisible Pages
Invisible Plugins
Conditional Content with no way to view or search it
XML-RPC activity by default, with no log, and cannot be disabled without editing a config file
Loose .htaccess files in subdirectories of /wp-content/.
As a consequence of Wordpress being a swiss army knife that allows the software to be used for Forums, Shopping Carts, and all manner of non-bloggy things, the security situation has gotten completely out of control and it doesn't seem like Wordpress is giving us any tools to fight.
At the very least, Wordpress needs:
Content Inspector that gives a bird's eye view of content that does not appear under Pages or Posts. Yes I understand people use Wordpress for Forums and Shopping Carts, etc. but there should still be a warts-and-all Content Inspector that lets you at least see and search for content in the database that might be malicious. There should be a judicious warning that deleting unrecognized content could break or cause data loss to third-party plugins.
Plugin Inspector which gives a bird's eye view of what's going on in /wp-content/plugins/. This would be a sort of File Manager type UI which flags directories and files which might not appear in the Plugins manager. It would display AND flag directories which aren't appearing in Plugins and flag dot (.) files as these shouldn't exist except for one .htaccess in the main dir. Plus git directories of course.
It should also be possible to view Multiuser (MU) Plugins and active plugin files from within the Plugin Inspector. None of this shows in subsites.
It should flag PHP files in /wp-content/uploads/. Hell, there should be a red banner across your site if a PHP file is found anywhere in /wp-content/uploads/.
Users Manager Upgrades. There should be a mechanism to display and manage ALL the Users on a Wordpress site. Right now it is trivial to create a phantom/hidden user with Admin access which does not appear in the Users Manager.
XML-RPC Manager. First, Wordpress should ship with XML-RPC turned off by default. Then, this new UI would allow turning it on and off within the UI, allow setting restrictions to specific whitelisted IP addresses, and finally display a log of recent requests.
Add Plugin Install/Update Queue. It should not be possible for an AJAX session alone to install or reinstall a plugin without any user intervention. All plugins should be required to be added to an install queue which has visibility in the Wordpress UI. Right now, plugin updates/installs happen behind the scenes with no visibility so you can clean up a site and be immediately reinfected. It needs to be possible to view as well as pause or stop the Plugin Install Queue.
Add a "Close All Admin Sessions" button which kicks every Admin out and requires them to relogin.
If you're wondering why all these suggestions are necessary, read this link:
It is now a relatively commonplace thing for a vulnerable plugin to install phantom plugins, create phantom users and grant them admin access, and then add phantom posts and pages which get indexed by Google and drive traffic all without ANY visibility within the Wordpress Admin UI. It's all completely invisible.

 Login