❌

Normal view

Why doesn’t WordPress have an app store like Apple, Google Play, or Shopify?

22 October 2026 at 22:35

WordPress.org has almost everything a mature platform needs, except a built-in marketplace for paid plugins. Instead, we have the free plugin directory, while premium plugins are sold independently across hundreds of different websites.

As a plugin developer, I sometimes feel WordPress is missing an opportunity here. The current model makes the premium ecosystem quite fragmented, with different stores, licenses, subscriptions, update systems, refund policies, and levels of trust.

A proper WordPress marketplace could potentially make discovering and buying premium plugins easier for users while giving developers a more reliable distribution channel.

Of course, centralising this also comes with downsides: platform fees, stricter rules, gatekeeping, and giving WordPress.org/Automattic more influence over the ecosystem.

Curious what others think. Would an official marketplace for premium WordPress plugins make the ecosystem better, or is the decentralised nature of WordPress actually one of its strengths?

EDIT:
Thanks for the downvotes; I get the concerns, but this is what I had in mind when I wrote the post.

Selling movie tickets or DVDs worked well, especially for established movies. But smaller or experimental films had a much harder discovery problem. Platforms like Netflix reduced some of that friction, so consumers could discover and try something unfamiliar with less perceived risk, while creators had another way to become discoverable.

Obviously there are pros and cons to centralization, and I'm not suggesting WordPress should copy Netflix or Apple's model.

My point is simpler: if there were a platform that reduced the risk and friction of purchasing premium plugins, while also helping smaller/new developers get discovered and build trust, I think there could be value for both sides.

The question is whether that can exist without taking away the independence that makes the WordPress ecosystem valuable in the first place.

submitted by /u/savydv
[link] [comments]

Unvetted AI Agents Are Accessing US Bank Accounts

By: BeauHD
22 October 2026 at 22:30
An anonymous reader quotes a report from Axios: Major U.S. banks are detecting unauthorized third-party AI agents operating inside customer accounts, with some agents attempting to take actions that appear to be independent of user instructions, sources tell Axios. The difficulty in distinguishing between a human and an unauthorized bot is forcing banks to block the technology and rapidly rewrite their terms of service. [...] This presents significant security risks: banking executives fear the steps agents with login access might take, especially if a user has granted purchase authority or the ability to shift funds. In other instances, some banks have tracked activity when agents -- programmed to fulfill requests or complete tasks on a user's behalf -- contact call centers or appear to take actions independent of user instructions, the people said. Bank executives described the situation as horrifying, with one official saying the industry has grave concerns about agents gaining access to customer accounts and taking steps that could impact user finances. The concerns are at the root of the decision by several banks to restrict third-party AI agent access, the people said. Morgan Stanley has begun blocking third-party agents from accessing its platforms, sources familiar with the decision said. JPMorgan, Bank of America and Citi are also restricting agents. [...] Many banks are broadly not able to parse whether agent account activity is user-directed, sources said. [...] On one hand, banks are best positioned to respond to the threats and opportunities of AI given their cash on hand and experience as critical infrastructure. But money isn't necessarily enough to solve this problem, one source said, because of how quickly the technology is developing and revealing new weaknesses in real time. Banks are investing in preventing worst-case scenarios, but they are also preparing for when those could happen, including with "day after" scenario planning that would allow them to quickly secure or restore customer access, sources said.

Read more of this story at Slashdot.

I spun up a free, read-only script to check WordPress sites for signs of PHP2Shell compromise. Looking for feedback

22 October 2026 at 21:58

Patching PHP fixes PHP2Shell (CVE-2026-109618 / 109619), but it does nothing about a backdoor someone planted before the patch. Amazon's honeypots caught an exploitation attempt on Oct 17, four days before disclosure, and Amazon's advice is to investigate from at least that date.

So I used Claude Code to spin up a bash script to triage WordPress sites. It checks:

* PHP CLI version vs. the fixed releases

* Core and plugin checksums (via WP-CLI)

* PHP files in uploads

* Files modified since Oct 17 (adjustable)

* auto_prepend_file hooks in .user.ini / .htaccess / php.ini

* mu-plugins

* Common web-shell patterns in wp-content

* Admin accounts and any users created in the window

* Injected scripts in options and posts

* WP-Cron, the site user's crontab, and SSH authorized_keys

It's read-only and never modifies or deletes anything. It runs WP-CLI with --skip-plugins --skip-themes so a backdoored plugin can't execute during the check. It works on one site, every site on a server, or a list of remote servers over SSH, and it writes a Markdown report per site plus a summary.

Repo (MIT): https://github.com/brentmartinmiller/php2shell-check

Caveats: a clean report lowers the odds of compromise but doesn't prove a site is clean. It doesn't parse web server logs, so pull those separately before rotation eats the Oct 17+ window. A few false positives are expected, like Wordfence's prepend file, header-script plugins, and obfuscated premium plugins. The README covers how to read them.

I'd appreciate feedback, especially false positives you hit, indicators I'm missing, or quirks on shared hosts. Issues and PRs welcome.

submitted by /u/82miles
[link] [comments]

GoDaddy PHP patching versions

22 October 2026 at 19:02

does anyone else who has sites hosted on GoDaddy notice that they only patched to 8.3.35, not 8.3.36? trying to get more information before I contact their support team. I have no control over where these certain few sites are hosted (I work at an agency, we do have a few stragglers left on GD)

submitted by /u/wutthefrak
[link] [comments]

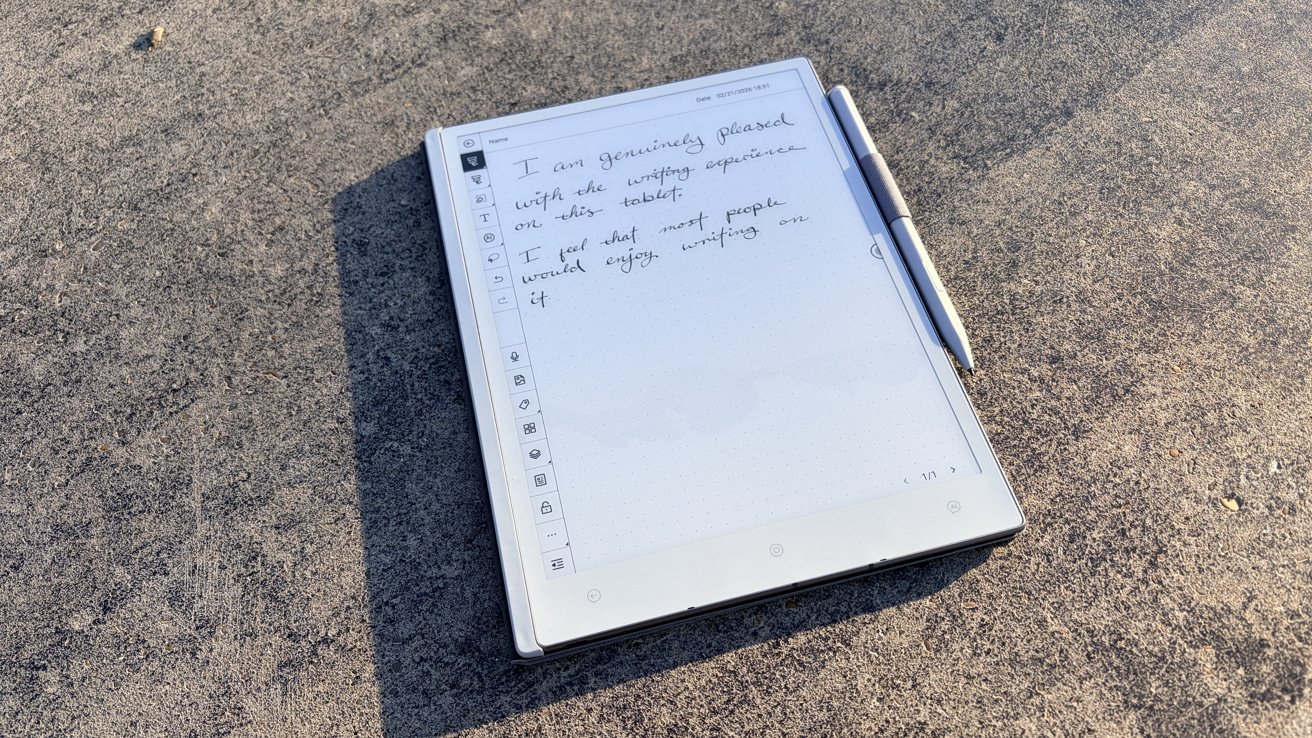
Viwoods AiPaper e-reader review: a damn fine digital notebook

Viwoods wants you to embrace artificial intelligence with its AiPaper e-reader — but I think it's actually banking on the wrong features.

E-ink writing tablet on rough concrete surface, displaying handwritten notes about enjoying the writing experience, with a stylus resting along the right side in bright outdoor sunlight
Viwoods AiPaper

The e-book reader market is growing, with plenty of companies offering their own takes on the genre.

Some, like most of Boox's lineup, offer an option that lies somewhere between a Kindle and an iPad. Others, like Durobo's Krono, want you to focus on portability over all else.


Continue Reading on AppleInsider | Discuss on our Forums

HALP! Overwhelmed by image compression options

22 October 2026 at 18:24

So I've read through like 4 million threads on here re: the best options for image compression on Worpress. Very long story short, I help run a music website and the vast majority of our contributors are concert photographers. We've taken to having people use their own personal IG pages and using the IG plugin for bulk photos and it's fine, but we still obviously need a few pictures per post that live on the site. I use Smush for now and it's fine but I feel like I need a way to batch-edit a large volume of .jpg images into something that'll take up a lot less space before the site caves in on itself. Again. I know there are probably 4 million directions people will point me in, but if there's a consensus of top 3/4 options that'll be easier to pare down.

Gracias, comrades.

submitted by /u/EmergencyCraft2562
[link] [comments]

To Make Way For Data Centers, Google Will Pay Others to Use Less Power

By: BeauHD
22 October 2026 at 18:00
Google is funding one of the nation's largest "virtual power plants," paying homes and businesses indirectly to reduce electricity consumption during periods of peak demand so more grid capacity can be available for data centers. Under its expanded deal with Voltus, the program could provide up to 1,070 megawatts in the Mid-Atlantic PJM grid -- roughly the output of a large nuclear reactor. The New York Times reports: That electricity won't come from new power plants. Instead, Voltus will sign up homes and businesses and give them financial incentives to curb their usage when local power demand is high or the grid is strained. Many of these reductions could occur automatically, such as through smart thermostats that dial back air-conditioning during peak summer hours or batteries that can provide temporary on-site power. Each of these tweaks frees up only a small amount of power on its own. But by aggregating them across thousands of businesses and homes, Voltus says it can reliably provide lots of extra capacity when it's most needed, and do so within a few years. While tech companies will likely ultimately need to build traditional power plants if they want to keep building large data centers, this approach could be a faster, cheaper and less-polluting option in the interim. "We really see virtual power plants as a critical short-term solution," said Ellen Zuckerman, head of energy market development for North and South America at Google. "It's a way to invest in our communities, really double down on our clean energy ambition, but also meet capacity at speed and scale."

Read more of this story at Slashdot.

Microsoft Says October Updates Didn't Actually Fix VPN Issues

By: BeauHD
22 October 2026 at 17:00
joshuark shares a report from BleepingComputer: Microsoft says it mistakenly flagged a bug causing Always On VPN connection issues as fixed in the October 2026 Windows 11 cumulative updates. Always On VPN replaced the legacy DirectAccess technology and supports domain-joined, non-domain-joined, and Microsoft Entra ID-joined devices running Windows 10, Windows 11, and Windows Server. It runs in the background and establishes secure tunnels back to the user's corporate network whenever their device connects to the internet. Microsoft first acknowledged the issue in a service alert sent to IT administrators in late September, saying it was triggered on systems running Windows 11 24H2 and later after installing the September 2026 security updates when the initial Always On VPN connection failed (e.g., when using automatic protocol selection with IKEv2 and SSTP). "When automatic protocol selection or protocol fallback was configured, affected VPN connections could remain stuck in a Connecting state or fail to connect after an initial connection attempt failed," it said. "In some cases, subsequent connection attempts could display the error, 'The specified port is already in use.'" After releasing the October 2026 Patch Tuesday Windows 11 cumulative updates, Microsoft marked the bug as resolved, but in a Tuesday update it said the issues weren't actually addressed and that a fix would ship later. "This disclosure was mistakenly updated to Resolved status on October 13, 2026. We have returned its status to Mitigated," it said in a service alert sent to IT admins. "A resolution for this issue is planned to be included in an update to be released in the coming weeks. We apologize for any inconvenience or confusion." While Microsoft continues working on a permanent solution, it shared a temporary fix that requires affected customers to choose one of two VPN tunneling protocols to work around the issue.

Read more of this story at Slashdot.

The Browser Company Retires Its Arc Browser, Pushes Users to Dia

By: BeauHD
22 October 2026 at 16:00
The Browser Company is shutting down its Arc browser on December 22 and encouraging users to migrate to Dia, its newer AI-powered browser for Apple Silicon Macs and Windows 11 PCs. Thurrott reports: In the message explaining why it was sunsetting Arc, The Browser Company explained that maintaining two separate browsers was difficult to justify, especially from a security perspective. "Dia was built from the ground up to meet today's security standards, so that's where our engineering and security teams will focus moving forward," the company wrote. The retirement of Arc will be gradual: While nothing changes for existing Arc users, it's no longer possible to create new Arc accounts as of today. On November 23, tab sync, Browse for Me, and other AI features will be disabled on the iOS and Android versions of Arc. Lastly, the desktop version of Arc will stop working on December 22, and Arc accounts will be deactivated.

Read more of this story at Slashdot.

Moderna Shares Plunge After Leak of Cancer Vaccine Data

By: BeauHD
22 October 2026 at 15:01
Moderna shares plunged as much as 25% after partial clinical trial data leaked for its personalized cancer vaccine developed with Merck, despite the full results showing promising outcomes for melanoma patients. Analysts attribute the selloff largely to inflated investor expectations rather than disappointing clinical results. CNBC reports: The personalized vaccine, known as intismeran autogene, paired with Merck's immunotherapy Keytruda reduced the risk of recurrence or death in certain melanoma patients by 42% compared with Keytruda alone. The data also showed the shot along with Keytruda reduced the risk of cancer spreading to distant parts of the body or death by 38%, compared with just the immunotherapy. The companies say about 82% of patients who received the personalized cancer vaccine alongside Keytruda were alive without their melanoma returning at two years, compared with 70% of those who received Keytruda alone. [...] Investors see the targeted vaccine as a possible breakthrough treatment, with the potential to be used in other forms of cancer in the future. It could also offer Moderna a critical additional commercial product in its pipeline, following vaccines for Covid-19, the flu and respiratory syncytial virus. "We assert this relative reduction in recurrence/death is clinically meaningful," said BMO Capital Markets analyst Evan Seigerman. "Such a reaction likely reflects inflated expectations into the full data release, rather than a true indictment on the efficacy of the combo therapy." UBS analysts said "this is overall a strong data set" and gives more confidence in upcoming studies of the vaccine in kidney and bladder cancers. They added the stock reaction may be due more to massive expectations than disappointing data.

Read more of this story at Slashdot.

Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

Attackers are exploiting a zero-day SQL injection flaw in Arista's VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw lets anyone who can log in to the orchestrator, even with a read-only customer account, gain operator privileges, the top level of control over it. For

Bose Is Buying Skullcandy

By: BeauHD
22 October 2026 at 14:00
An anonymous reader quotes a report from Wired: Longtime audio giant Bose announced on Wednesday that it's acquiring Skullcandy, the lifestyle brand known for its bass-heavy headphones. Skullcandy will remain a separate company within Bose's Premium Consumer Audio business and will still be based in Park City, Utah. The acquisition isn't out of left field. Bose has lent its audio expertise to Skullcandy over the past year under its Sound by Bose licensing program. Skullcandy designs the headphones and then works with Bose on the audio front. The relationship began with the Skullcandy Method 360 ANC earbuds in 2025 and more recently, with the Crusher 1080 ANC headphones in July. [...] This is hardly Bose's first audio acquisition (though it may be the most mainstream). Bose acquired McIntosh Group, owners of luxury audio brands McIntosh Laboratory and Sonus Faber, back in 2024. But Bose seems to be after Skullcandy's connection to its community. "What does the brand stand for? Does it have meaning for consumers? Is it relevant to a group of consumers that, frankly, we otherwise aren't reaching?" Bose CEO Lila Snyder tells WIRED. "If you think about McIntosh, Sonus Faber, and Skullcandy, they all fit into that realm. Skullcandy gives us access to a customer base that we think we're largely missing with the Bose brand." That's why Bose has no plans to relocate Skullcandy from Park City, Utah, which Snyder says is the epicenter of board sports culture. "We want to make sure we're right at the heart of it, as they always have been," she says. Skullcandy products are also affordable, especially compared to other Bose products and Bose-owned brands, which lets Bose compete at both ends of the market.

Read more of this story at Slashdot.

eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable

eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates. eMudhra said it will replace affected customers' certificates with free ones from partners, though its

ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More

This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That's a lot to deal with in just a few days. And the week isn't even over yet. But those big headlines are only half the story. Stolen passwords, exposed

Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes

Linux servers running KSMBD, the kernel's built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro's Zero Day Initiative, with no fix yet in the mainline kernel. One of them, ZDI-CAN-33774, can be triggered before any network authentication. The other, ZDI-CAN-33549, requires the SMB Direct transport and an RDMA-capable network

Zoe Kleinman: PHP Is the Cyber Equivalent of an Unexploded Bomb

By: BeauHD
22 October 2026 at 13:00
BBC technology editor Zoe Kleinman likens the recently discovered PHP security vulnerabilities to an unexploded bomb, writing, "The PHP story feels like the cyber equivalent of an unexploded bomb -- I have never seen such a dramatic, public and global response to a cyber event that hasn't happened yet." Although no successful attacks have been confirmed, the AI-assisted discovery of long-hidden flaws has triggered a worldwide security scramble, with websites taken offline as a precaution and administrators racing to deploy patches before attackers can exploit the vulnerabilities. From the report: The weaknesses found in the PHP programming language, which is used by millions of websites, had been quietly resting there for years and are not easy to exploit. One cyber security researcher told me he'd been up all night trying to do it as an experiment, but it was proving very difficult. [...] It was supposed to be kept quiet until everyone had a chance to fix their sites -- but the news was leaked. From that point the clock started ticking. As I write this, there are no reports that anyone or anything has succeeded in using the flaws to attack a site. "There's a real dilemma," said Prof Alan Woodward from Surrey University. "How do you alert people they need to be ready, and then that a patch is urgently required, whilst not alerting attackers? Basically you're telling everyone about the problem at the same time and hoping the defenders aren't awake enough to act as soon as the patch is out." But we do know from large web companies like Cloudflare and Palo Alto Networks that millions of attempts have been made. We probably won't know for a while whether it has worked for any criminals, because the companies affected might not be aware yet either. As far as we know the unexploded bomb remains intact for now, and for some experts this is a success. "We've seen how a team of people supported by the large AI company have used AI to find the problem, work for months together to solve it and get everybody ready to be safe and secure," Gina Neff, Professor of Responsible AI at Queen Mary University, told the Today Program on BBC Radio 4. "We have enormous capability to handle these risks."

Read more of this story at Slashdot.

[PROMO] Claude made changing my WordPress site so easy I stopped checking whether my changes actually worked.

22 October 2026 at 12:34

I’m pretty AI-pilled. Claude does most of my website updates now: headlines, landing pages, Woo order updates, bugfixes. Its so fast, but that created a new problem. Changing things got so easy that I was shipping update after update without knowing whether any of them helped or hurt conversions.

So I wrote two open-source agent skills that teach the AI when a change needs to be measured and what to measure.

prove-website-changes Stops AI from blindly publishing changes that might affect conversions. It proposes an A/B test instead.

website-optimisation-loop - Actively finds opportunities using reviews, analytics, best practice and heatmaps, runs experiments, and learns from the results.

Both are plain Markdown and MIT licensed. They work in Claude Code, Hermes, Codex, Grok Bot or anything that loads skills.

https://github.com/SiteSpot/human-web-feedback-loop

Disclosure: I make AB Split Test, and it’s the default testing tool in the skills. The free works fine for this. If you already use Optimizely, VWO, PostHog, GrowthBook or similar, connect its MCP server and the skills will use that instead.

Anyone else letting AI make changes to their live sites? How are you checking that it’s actually helping?

submitted by /u/tomdoinit
[link] [comments]

Anthropic Takes On Muse With Claude Duet

By: BeauHD
22 October 2026 at 12:00
Anthropic has launched Claude Duet, an AI agent aimed at professionals and small businesses that competes with Meta's Muse and OpenAI's Dots. Here's Anthropic's description of what it can do: Each morning, it sends you a short brief on the most important items across your connected apps. Throughout the day, it keeps tabs on those apps and messages you only when something needs your attention. You can also hand it tasks of all shapes -- from simple administrative tasks of scheduling meetings to more complex ones, such as building dashboards with dozens of tools, creating financial or sales forecasts, prototyping, and building web apps. The Verge reports: Claude Duet pulls in memory, skills, and connected apps from Claude, and it has a virtual machine with a browser that it can use for completing work. Before any big step, like sending a payment or deleting something, Claude Duet messages you for approval. Given that Duet may be taking action on sensitive information, it has a new "new dedicated classifier and safety system prompt" that are "designed to reject requests to share the strictest tier of information," such as credit card numbers. Anthropic says Claude Duet is currently an "early version" and that it "still might misread a thread or miscalibrate what's urgent." It's also not "as strong" at personal errands like booking tickets.

Read more of this story at Slashdot.

❌